On This Page
Submit a Certificate Signing Request
Follow these steps to submit your own public PEM-formatted certificate signing request (CSR).
- Log in to theSmartpay Fuse Portal:
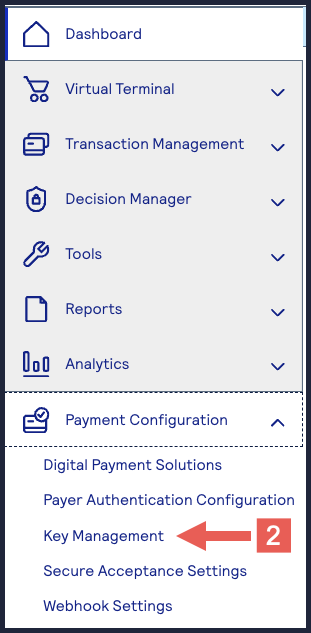
- On the left navigation panel, choose
 Payment Configuration > Key Management.
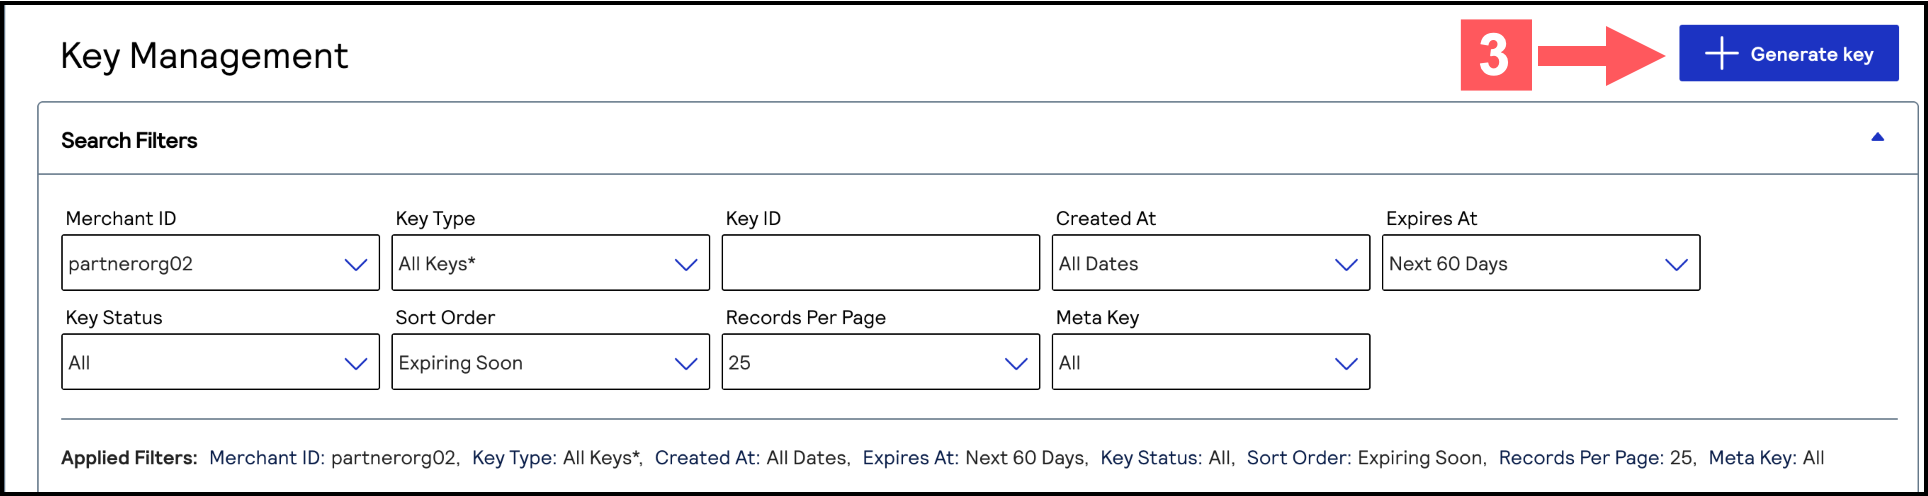
- Click+ Generate keyon the Key Management page.
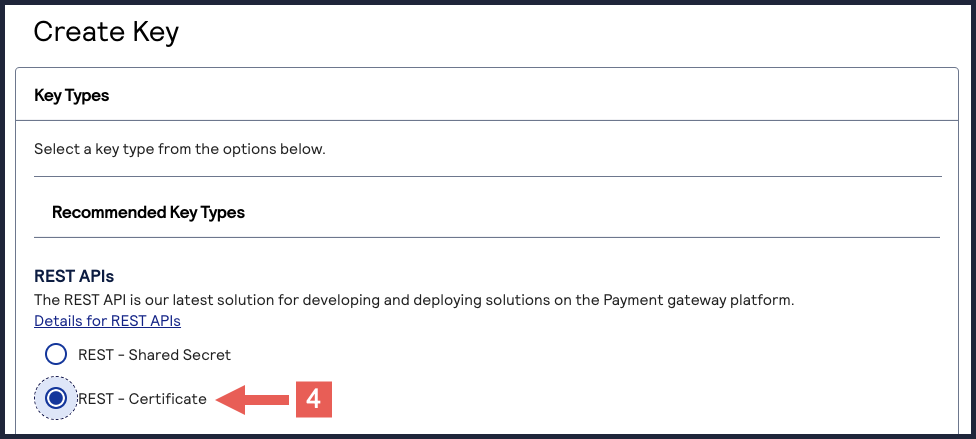
- Under REST APIs, chooseREST – Certificate, and then clickGenerate key.The Key Generation page appears.If you are using aportfolioaccount, the Key options window appears, giving you the choice to create a meta key.
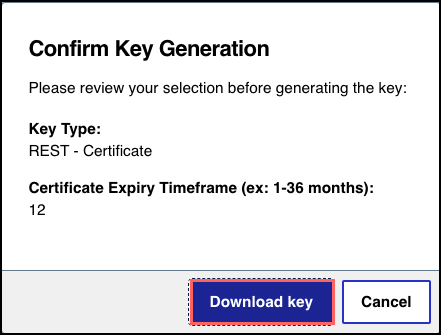
 The Confirmation Key Generation window appears.
- ClickDownload keyafter reviewing the key details.
 The Key Generation page appears.
- (Optional) You can set the Certificate Expiry Timeframe field to the number of months you want the key to remain active before it expires. Only whole numbers from 1–36 are accepted. By default, new keys expire after 12 months.
- Enter your public PEM-formatted certificate in the text box, then clickDownload key
 .If you need to generate your own CSR and private key, run this command. In this example,merchantis your organization or merchant ID (MID). You can extract the certificate value by opening theexample.csrfile using a text editor application.openssl req -new -newkey rsa:2048 -keyout private_key.pem -out example.csr -sha256 -nodes -subj "/CN=merchant"
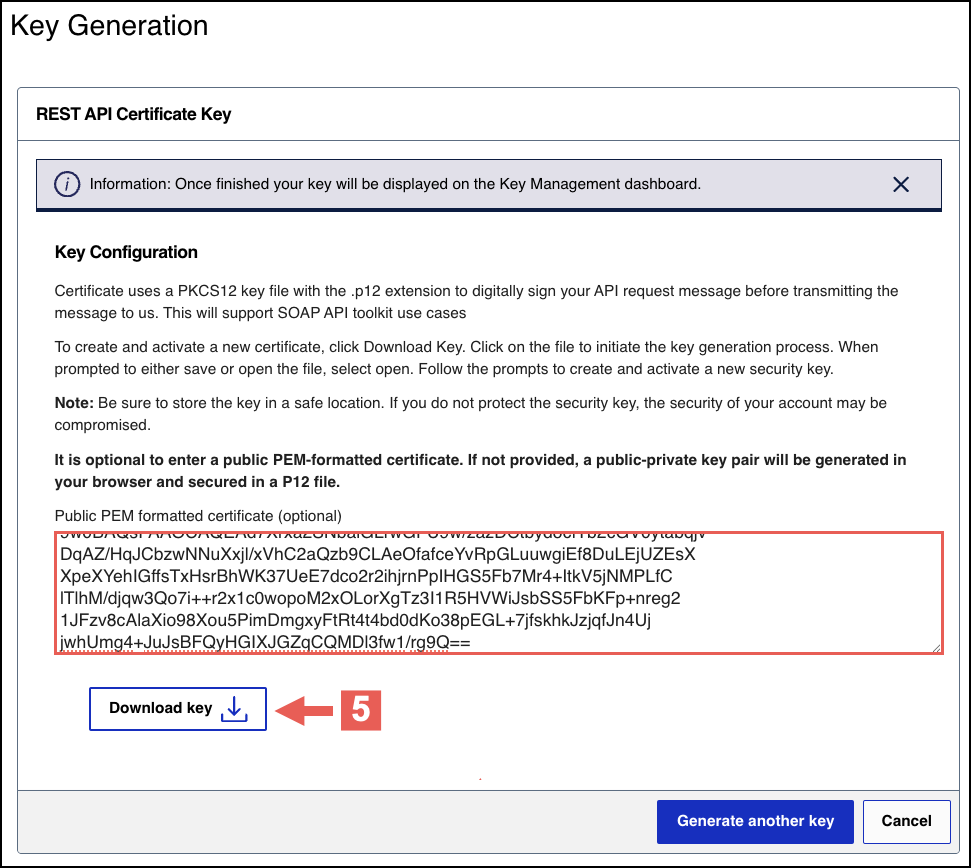
- (Optional) To convert your submitted CSR into a.p12file, run this command. In this example,merchantis your organization or merchant ID (MID).You can use the P12 certificate for testing using theREST API Referenceon the Developer Center.openssl pkcs12 -export -name "$(printf 'serialnumber=%s,cn=%s' "$(openssl x509 -inmerchant_certChain.pem -noout -serial | cut -d= -f2 | xxd -r -p)" "$(openssl x509 -inmerchant_certChain.pem -noout -subject | sed -n 's/.*CN=\([^/]*\).*/\1/p')" )" -outmerchant.p12 -inkey private_key.pem -inmerchant_certChain.pem
- When prompted, set a password for the.p12file.
To create or upload another key, click
Generate another key
. To view
all of your created keys, go to the Key Management page.IMPORTANT
Securely store the
.p12
file and password in your system.
These credentials are required in order to implement certain products, and you must
be able to access them.